
White Box Penetration Testing
Maximum Visibility. Maximum Testing Depth.
What Is White Box Penetration Testing
- Manual, in-depth security testing
- Authenticated and unauthenticated testing
- Source code and configuration review where applicable
- Multiple user roles and privilege levels
- Deep business logic and authorization testing
- Clear technical findings and remediation guidance
- Remediation testing included
Maximizing Value of SOC 2 Penetration Testing
User Role/ Authenticated Testing
We perform a thorough penetration test of your web application across its functionality and user roles using OWASP ASVS and OWASP Top 10. For applications with AI or agentic functionality, we assess relevant AI security risks and attack paths.
Mobile
If your web app has a mobile side, it may be valuable to test the interaction between them. Our testing evaluates communication security using our methodology based on OWASP ASVS, OSSTMM, and PTES.
API
API testing is often done in conjunction with web penetration tests. APIs can be a weak vector into any organization that doesn’t check its security. We leverage OWASP’s research to find the most common attack vectors.
Cloud
Your web application sits on top of infrastructure, and even it is in the cloud, it is important to test. Our experts have deep experience in all major cloud providers and follow their terms of service to ensure no interruption: AWS, GCP, Azure, and Oracle. This gives you the opportunity to dive deep into your application’s infrastructure.
Code Review
A code review is the best way to check for vulnerabilities before they are seen by the public. It can also catch business logic flaws and other problems that are not readily apparent in the compiled application. We utilize OWASP’s Code Review Guide and Google’s Standard of Code Review
Internal & External Network Testing
We assess both internal and external network environments to identify weaknesses that could expose critical systems and sensitive data. External testing evaluates your internet-facing attack surface, while internal testing simulates threats from within the network or from an attacker who has gained an initial foothold.
Assets That Could Be Tested
-
Web Applications
Perform comprehensive testing of authenticated and unauthenticated functionality across user roles, permissions, workflows, business logic, application architecture, and security controls. -
APIs
Assess APIs using credentials, authentication tokens, documentation, endpoint definitions, and relevant implementation details to identify authorization, authentication, data exposure, injection, business logic, and configuration vulnerabilities. -
Mobile Applications
Assess iOS and Android applications, backend services, API communication, authentication flows, local storage, application logic, and security controls with access to relevant documentation, credentials, and implementation details where included in scope. -
Internal Networks
Assess the internal environment with authorized network access and relevant environment information. Testing can evaluate privilege escalation, lateral movement, segmentation, identity infrastructure, exposed services, access controls, trust relationships, and potential paths to critical systems. -
External Networks
Evaluate internet-facing infrastructure with knowledge of the approved environment, allowing testers to systematically assess exposed systems, services, configurations, and potential attack paths. -
Cloud Environments
Assess cloud infrastructure using authorized access to evaluate identity and access management, permissions, configurations, exposed resources, trust relationships, privilege escalation paths, and potential access to sensitive systems and information.
How CYBRI Penetration Testing Works
CYBRI Pen Tests are on-demand hacker-powered penetration tests performed by one or two Red Team members. You pay a fixed price for your test and we do the rest. You can always increase the frequency.
Discovery
We will collect the needed information from you and your team to make sure that the right assets are being tested and the right team is assigned.
RED TEAM IN ACTION
CYBRI Red Team members will start testing your infrastructure and will ensure coverage of OWASP top 10 vulnerabilities. They will utilize their own techniques to ensure the highest levels and standards of testing.
Reporting
Collaboration
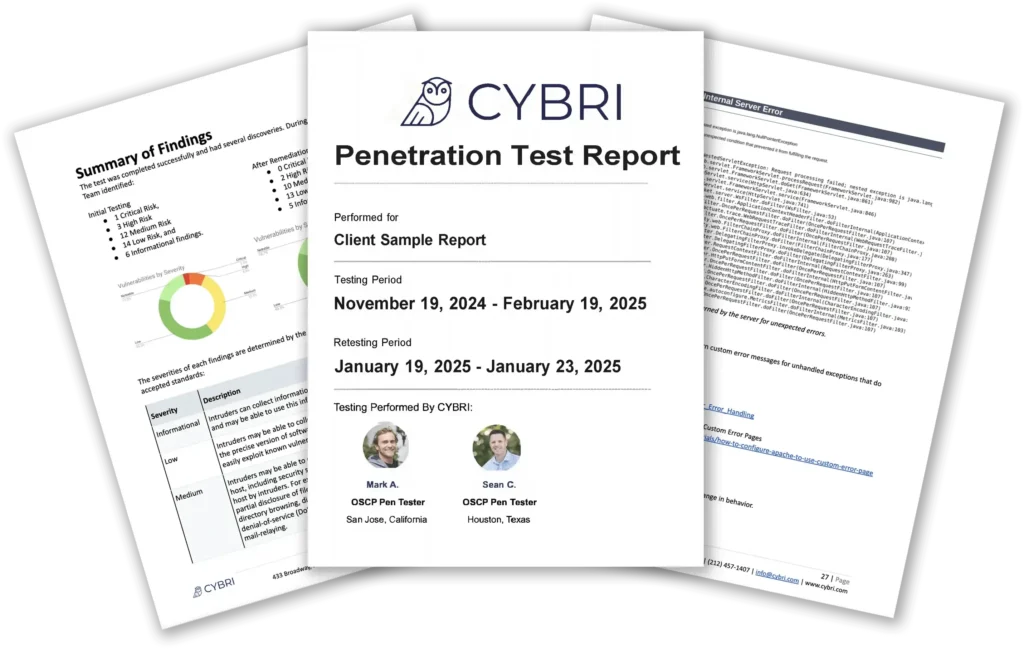
After each finding is verified by our Red Team members, they get submitted into your dashboard and report. Upon completion of each test, you will have a clear report that can be shared with executive and technical members as well as your clients.
Retest
Once the findings have been remediated by your team and the time is right to retest your technology, you can easily do so by scheduling a new test with us or by purchasing an annual package of multiple tests.
Repeat
Improve risk posture and decrease the liability of your organization. Asses the cybersecurity and risk of your organization on an annual engagement basis with the top five percent of the nation’s cybersecurity talent, the CYBRI Red Team.
We spend a week or more preparing before we execute. We will collect the needed information from you and your team to make sure that the right assets are being tested and the right team is assigned.
CYBRI Red Team members will start testing your infrastructure and will ensure coverage of OWASP top 10 vulnerabilities. They will utilize their own techniques to ensure the highest levels and standards of testing.
Communicate with CYBRI Red Team members about your vulnerabilities and assign the vulnerabilities for remediation to your team members; all directly in our platform. Our platform has a clear collaboration functionality to help your team with remediation of the findings.
After each finding is verified by our Red Team members, they get submitted into your dashboard and report. Upon completion of each test, you will have a clear report that can be shared with executive and technical members as well as your clients.
Once the findings have been remediated by your team and the time is right to retest your technology, you can easily do so by scheduling a new test with us or by purchasing an annual package of multiple tests.
Improve risk posture and decrease the liability of your organization. Asses the cybersecurity and risk of your organization on an annual engagement basis with the top five percent of the nation’s cybersecurity talent, the CYBRI Red Team.
How White Box Pentest Works
1. Scope The Engagement:
2. Provide Test Access:
Your team provides the access and technical information required for the agreed engagement. Depending on the scope, this may include:
- Test accounts for relevant user roles
- Application URLs and IP addresses
- API credentials or authentication tokens
- API documentation
- Source code repositories
- Architecture and network diagrams
- VPN or internal network access
- Cloud test accounts or defined permissions
- Configuration files
- Technology and environment documentation
- Allowlisting requirements
3. Manual Penetration Test:
4. Findings And Remediation:
5. Remediation Testing:
How Long Does a White Box Pentest Take
Most white box penetration tests can be completed within 5–15 business days, depending on the size, complexity, and depth of the environment being assessed. Smaller applications or environments may require less time, while engagements involving large codebases, multiple applications, APIs, user roles, networks, cloud environments, or extensive architecture may require additional testing time.
Your expected testing duration is defined during scoping before the engagement begins.
How Much Does White Box Penetration Testing Cost
- Number and type of assets
- Application size and complexity
- Number of authenticated user roles
- Number of APIs and endpoints
- Source code size and complexity
- Internal or external network size
- Cloud environment complexity
- Mobile platforms
- Engagement objectives and testing depth
Grey Box vs. Black Box vs. White Box Penetration Testing
Approach | Black Box | Grey Box | White Box |
Prior Knowledge | Minimal | Partial | Extensive |
Credentials Provided | No | Yes, where required | Yes |
Multiple User Roles | Usually No | Usually Yes | Yes |
Internal Documentation | Minimal / None | Relevant Information | Extensive |
Source Code Access | No | Usually No | Yes |
Unauthenticated Testing | Yes | Yes | Yes |
Authenticated Testing | No | Yes | Yes |
Authorization Testing | Limited | Extensive | Extensive |
Business Logic Testing | Limited | Extensive | Extensive |
Attacker Perspective | External Attacker | External + compromised/legitimate user | Full-access assessment |
Testing Efficiency | Lower | High | High |
Benefits of White Box Penetration Testing
White box testing provides the greatest level of visibility and testing depth by giving security professionals access to information that would normally be unavailable to an external attacker.
9 Years Dedicated To Penetration Testing
Since 2017, CYBRI has been dedicated to penetration testing, helping businesses of all sizes, from startups to multinational enterprises, identify and eliminate security vulnerabilities. Our sole focus is pentesting and vulnerability scanning, ensuring deep expertise and rigorous assessments without distractions.
What Our Customers Have to Say
What to Expect During a White Box Penetration Test
-
Manual-First Testing
Our security professionals manually investigate your environment rather than relying exclusively on automated vulnerability scanners. Automated tools may support the engagement, but findings are manually validated and explored to understand their real security impact. -
Deep Environment Visibility
Our testers use the technical information and access provided during the engagement to systematically assess the environment beyond what is visible from the outside. This allows testing to focus on security-critical functionality, configurations, architecture, privilege boundaries, and implementation weaknesses that may not be reachable during black or grey box testing. -
Source Code & Configuration Analysis
Where source code or configuration review is included in scope, our testers analyze security-relevant implementation details and correlate potential weaknesses with the behavior of the running environment. This can help identify vulnerable code paths, insecure configurations, unsafe implementation patterns, and weaknesses that may be difficult to discover through dynamic testing alone. -
Testing Across User Roles
Where multiple roles exist, we evaluate whether permissions and authorization boundaries are properly enforced. This helps identify vulnerabilities where one user may be able to access information, functionality, or administrative actions intended for another role. -
Real-World Attack Paths
Individual vulnerabilities do not always represent the full risk. Our testers investigate whether weaknesses can be combined to create more significant attack paths, including unauthorized access, privilege escalation, sensitive data exposure, or compromise of additional systems. -
Communication During Testing
You are not left waiting until the end of the engagement to learn about serious security issues. Critical vulnerabilities can be communicated to your team during testing so remediation can begin immediately. -
Controlled Testing
Testing is performed only against the agreed scope and according to the engagement rules established before testing begins. We do not perform destructive actions, intentionally disrupt production systems, modify critical data, or expand testing outside the approved scope without your authorization. -
Clear Reporting
At the end of the engagement, you receive a penetration testing report designed for both technical and business stakeholders. The report includes:
- Executive summary
- Scope and methodology
- Risk-rated findings
- Affected assets
- Technical evidence
- Business impact
- Reproduction details
- Remediation guidance
- Compliance Mapping
Compliance Testing
Remediation Testing and Support
9 Years Dedicated To Penetration Testing
Since 2017, CYBRI has been dedicated to penetration testing, helping businesses of all sizes, from startups to multinational enterprises, identify and eliminate security vulnerabilities. Our sole focus is pentesting and vulnerability scanning, ensuring deep expertise and rigorous assessments without distractions.
Get a SOC 2 Pentest Quote