Web Application Penetration Testing Services
CYBRI’s web application penetration testing services cover web and mobile applications, APIs, cloud environments, networks, and AI systems, including customer-facing and internal agentic applications. CYBRI’s reports are built to support SOC 2, ISO 27001, HIPAA, GDPR, and other compliance requirements.
Every web application penetration test includes remediation testing and support.
CYBRI Web Application Penetration Testing
CYBRI helps engineering and DevOps teams identify critical vulnerabilities, support compliance with clear evidence, remediate issues faster, and meet pentesting requirements that help unlock larger deals.
Benefits Of Working With CYBRI
Since 2017, CYBRI has applied established OWASP and NIST methodologies to help organizations identify web application vulnerabilities.
CYBRI Red Team
CYBRI’s Red Team consists of experienced OSCP and OSWE-certified web application penetration testers.
Detailed Reporting
Easy-to-understand penetration testing reports that can be shared among your executive and technical teams.
Compliance Support
SOC 2, ISO 27001, HIPAA, and GDPR vulnerability mapping with clear evidence and actionable remediation guidance.
Maximizing Value Of Web Application Penetration Testing
User Role/ Authenticated Testing
We perform a thorough penetration test of your web application across its functionality and user roles using OWASP ASVS and OWASP Top 10. For applications with AI or agentic functionality, we assess relevant AI security risks and attack paths.
Mobile
If your web app has a mobile side, it may be valuable to test the interaction between them. Our testing evaluates communication security using our methodology based on OWASP ASVS, OSSTMM, and PTES.
API
API testing is often done in conjunction with web penetration tests. APIs can be a weak vector into any organization that doesn’t check its security. We leverage OWASP’s research to find the most common attack vectors.
Cloud
Your web application sits on top of infrastructure, and even it is in the cloud, it is important to test. Our experts have deep experience in all major cloud providers and follow their terms of service to ensure no interruption: AWS, GCP, Azure, and Oracle. This gives you the opportunity to dive deep into your application’s infrastructure.
Code Review
A code review is the best way to check for vulnerabilities before they are seen by the public. It can also catch business logic flaws and other problems that are not readily apparent in the compiled application. We utilize OWASP’s Code Review Guide and Google’s Standard of Code Review
Black Box/ Unauthenticated Testing
For our most veteran customers, black box testing provides testers with only the URLs in scope. The goal here is to uncover as much information as possible with just the bare minimum to start to best simulate an attack in the real world.
Remediation Testing and Support
Every CYBRI web application penetration test includes remediation testing and post-report support. Most clients continue working with us for five years or longer.
What Our Customers Have to Say
Security, Compliance, & Customer Requests:
- Functionality releases – Ensure each release of your application is secure as they get released, as opposed to waiting. Get tested before your release goes public.
-
Compliance - Whether you need to comply with:
• SOC 2
• HIPAA
• ISO 27001
or other compliance standards, getting a pen-test will help you meet those requirements. - Vendor/Customer Requests - Customers, partners, and vendors may require application penetration testing to validate your security posture and confirm that appropriate safeguards are in place to protect their data. CYBRI follows established methodologies including OWASP ASVS, OSSTMM, and PTES to provide clear, credible testing results.
- Security Awareness - Pen testing your application will ensure you know where you stand in comparison to industry standards and get the peace of mind you need, such as knowing you have no vulnerabilities in the OWASP Top 10.
- Intrusion Prevention - Application pen testing can reduce your attack surface, which significantly reduces the likelihood of compromise.
The Attack Vectors We Test:
- Broken Access Control where the validation of access does not properly validate all conditions and can allow access to areas where the user was not meant to go or allows for privilege escalation.
- Cryptographic Failures is a common problem where the protocols and cipher suites that are used are insecure, or that secure communication channels can be bypassed.
- Injection includes any ability to have inputs process data improperly, namely to be run as a line of code. This includes the very common and famous SQL injections and Cross-site scripting vulnerabilities.
- Insecure Design is a new focus, different from insecure implementation, where the flaw is logical and often rooted in the application's code structure and not a specific vulnerability with a patch. These require more intensive testing and remediation.
- Security Misconfiguration features many basic problems that are still left by the application designers. This includes default passwords, unnecessary features, overly verbose errors, default or lack of security controls.
- Vulnerable and Outdated Components are probably the most commonly known attack vector, as these can be easily found by a scanner. The importance of testing is to ensure that these findings are legitimate and do not impact other components. This can include third-party tools, libraries, packages, and programs.
- Identification and Authentication Failures is also a commonly found weakness, where the authentication itself is insecure. This can be the allowance of brute-forcing, weak password requirements, insecure password change systems, or exposure of authentication details such as session tokens.
- Software and Data Integrity Failures are when the data is exposed and does not have sufficient validation of its integrity, allowing attackers to be able to modify it unbeknownst to the owners. This can be caused from an insecure CI/CD pipeline, allowing for malicious code or access. This includes supply chain compromise
- Security Logging and Monitoring Failures is not often covered by a pen test but usually falls within a secure configuration review. Logging is often a too little, too late problem where victims don’t know they didn’t have it until something bad happens.
- Server-Side Request Forgery is not a common attack vector, but it is gaining in popularity. This is often when a web application is fetching an unvalidated remote resource, and that is subject to redirection to a malicious server. This can bypass a firewall, WAF, or other protection.
Why Companies Choose CYBRI
CYBRI has performed hundreds of web application penetration tests for organizations ranging from early-stage startups to multinational companies. We support clients through remediation with clear findings, practical recommendations, and remediation testing.
Each engagement is scoped around the frontend and backend technologies, architecture, user roles, business logic, and compliance requirements. This allows our team to provide clear evidence and practical remediation recommendations that engineering and DevOps teams can act on efficiently.
What To Expect During An App Pen Testing:
- Manual-first penetration testing performed by OSCP and OSWE certified security experts specializing in application security.
- Access to experts for guidance, questions, and remediation support throughout the engagement.
- Clear executive and technical reports that leadership and engineering teams can act on, with the depth needed to support remediation and compliance.
Assessments
Penetration Testing as a Service (PTaaS) by CYBRI
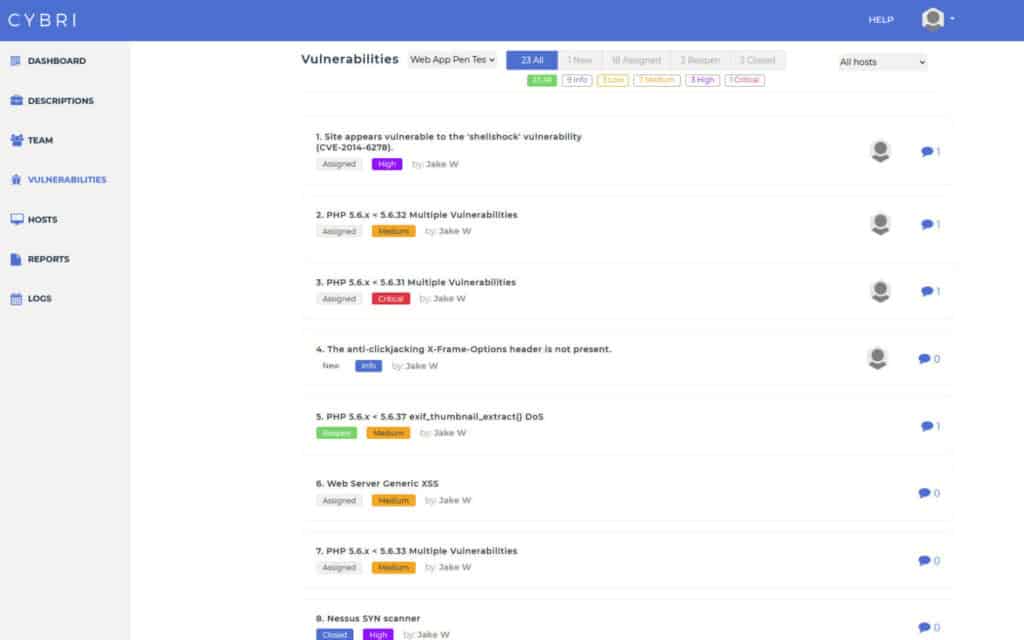
Our PTaaS offering gives clients direct access to CYBRI’s Red Team through Blue Box to review evidence, collaborate on remediation, and manage penetration testing engagements in one place.
How CYBRI Penetration Testing Works
CYBRI’s web application penetration testing is manual-first and performed by experienced Red Team members. Clients can choose a fixed-scope engagement with pricing defined upfront or a PTaaS model with prepaid testing capacity for ongoing assessments, retesting, and changing application needs.
Discovery
We will collect the needed information from you and your team to make sure that the right assets are being tested and the right team is assigned.
RED TEAM IN ACTION
CYBRI Red Team members will start testing your infrastructure and will ensure coverage of OWASP top 10 vulnerabilities. They will utilize their own techniques to ensure the highest levels and standards of testing.
Reporting
Collaboration
After each finding is verified by our Red Team members, they get submitted into your dashboard and report. Upon completion of each test, you will have a clear report that can be shared with executive and technical members as well as your clients.
Retest
Once the findings have been remediated by your team and the time is right to retest your technology, you can easily do so by scheduling a new test with us or by purchasing an annual package of multiple tests.
Repeat
Improve risk posture and decrease the liability of your organization. Asses the cybersecurity and risk of your organization on an annual engagement basis with the top five percent of the nation’s cybersecurity talent, the CYBRI Red Team.
We spend a week or more preparing before we execute. We will collect the needed information from you and your team to make sure that the right assets are being tested and the right team is assigned.
CYBRI Red Team members will start testing your infrastructure and will ensure coverage of OWASP top 10 vulnerabilities. They will utilize their own techniques to ensure the highest levels and standards of testing.
Communicate with CYBRI Red Team members about your vulnerabilities and assign the vulnerabilities for remediation to your team members; all directly in our platform. Our platform has a clear collaboration functionality to help your team with remediation of the findings.
After each finding is verified by our Red Team members, they get submitted into your dashboard and report. Upon completion of each test, you will have a clear report that can be shared with executive and technical members as well as your clients.
Once the findings have been remediated by your team and the time is right to retest your technology, you can easily do so by scheduling a new test with us or by purchasing an annual package of multiple tests.
Improve risk posture and decrease the liability of your organization. Asses the cybersecurity and risk of your organization on an annual engagement basis with the top five percent of the nation’s cybersecurity talent, the CYBRI Red Team.
Tell us about your assets and testing requirements and we’ll come back with a scope and a fixed price.
- Testing run by OSCP-certified experts
- Reports mapped to SOC 2, ISO 27001, HIPAA, PCI DSS, and GDPR
- A cloud-based platform where you track findings and collaborate on fixes as they land
- Remediation testing
Discuss Your Project