You asked a few providers for a PTaaS (penetration testing as a service) quote, and the numbers came back in shapes you cannot line up: one a single flat fee, one an hourly rate with no clear total, and one a bucket of “credits” to spend over the year. The testing itself is roughly the same work; the way you pay for it is not. This article explains the three PTaaS pricing models in plain terms and shows which models keep your budget predictable and which can quietly run higher than you planned.
Quick Answers
What’s the difference between fixed-price, hourly, and credit-based PTaaS?
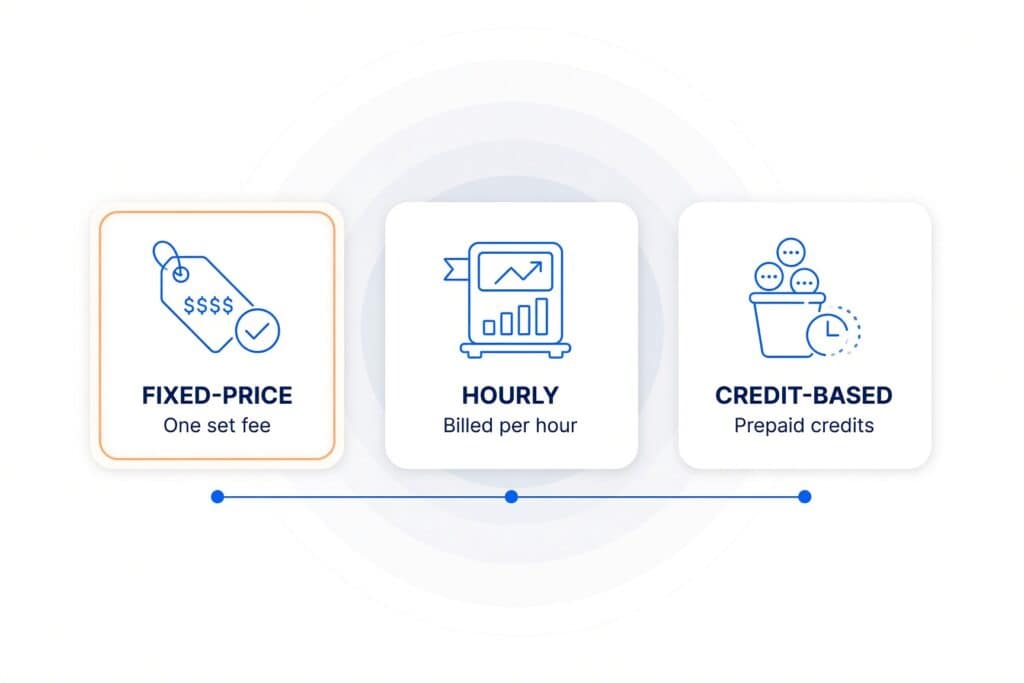
Fixed-price is one agreed fee for a defined scope, set before the work starts. Hourly (time and materials) bills for the hours the testers put in, with no set total. Credit-based is a prepaid bucket of credits you buy up front and spend on testing across the year.
Which PTaaS pricing model should I choose?
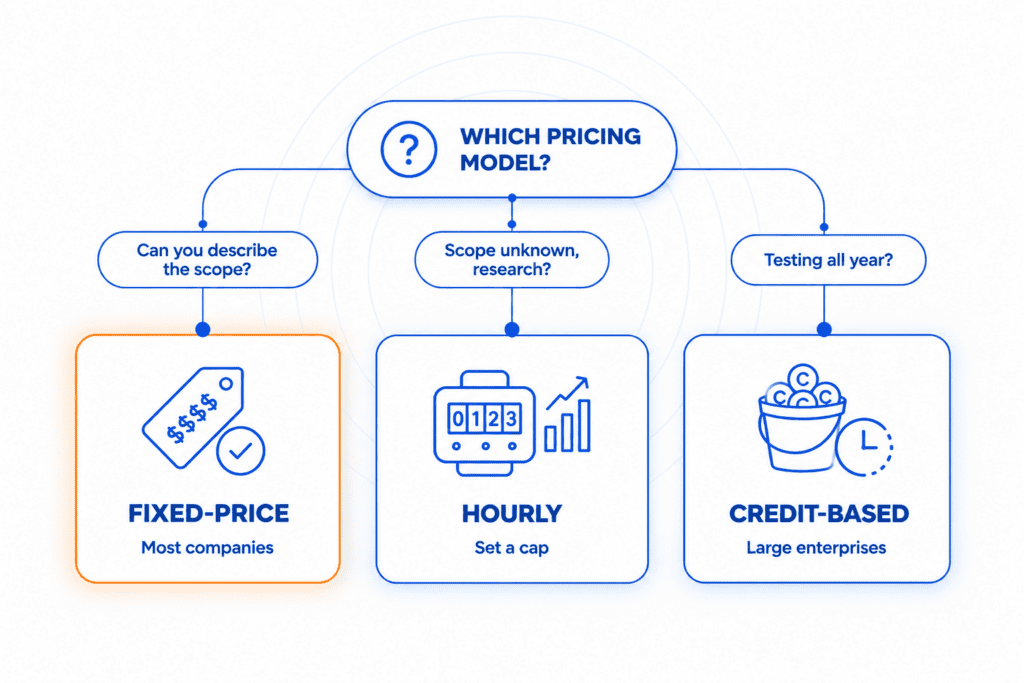
For a defined test or a compliance deadline, which covers most buyers, fixed-price is the safest pick: you know the full cost before anyone starts. Hourly suits open-ended research where the scope is unknown. Credit-based fits large enterprises that test constantly and will use every credit they buy.
How much does PTaaS cost?
Cost tracks scope, not the pricing model. A single web application test commonly starts around $5,000, and the price scales up from there as you add APIs, cloud accounts, or more apps to the scope. See CYBRI’s pricing page for current ranges.
Which pricing model has hidden costs?
Hourly is the one to watch: with no ceiling, the bill can climb well past the estimate. Credit-based can waste money too, since unused credits usually expire at the end of the year. A fixed price is the only one of the three with no surprise at the end.
The Three Models, in Plain Terms
First, a quick clarification, because the word “PTaaS” gets used loosely. Penetration testing as a service is a delivery model: the testing is run through a platform you log into, with results, retests, and history kept in one place, rather than a one-off project that ends with a PDF. Because your software keeps shipping, PTaaS is usually bought as a series of engagements across the year, matched to your release schedule, where you prepay a defined scope and add new features or services to it as they go live. How you are billed for it, a flat fee, an hourly rate, or a bucket of credits, is a separate question, and that is the one this article compares.
All three models buy the same testing. They differ only in how the meter is set.
Hourly, or time and materials. You pay for the hours the testers work, plus any tools, at the vendor’s hourly rate. It behaves like a taxi meter: fair when you genuinely cannot define the trip, but with no fixed destination the fare is whatever it adds up to. That suits open-ended research where nobody can scope the work in advance. For a normal app or compliance test, where the scope is knowable, it mostly removes your cost ceiling and gives the vendor a reason to take longer.
Credit-based, flexibility in the abstract. You buy a bucket of credits up front and spend them through the year on different tests, the way a prepaid phone plan works. For a large enterprise with constant, varied testing, that flexibility is genuine. The catch is two-sided: a “credit” is really a price list wrapped in an abstract unit, which quietly makes comparing one vendor against another harder than it should be, and whatever you have not spent by the renewal date usually expires. Flexibility you pay for and then forget to use is just waste.
Fixed-price, the one most buyers want. You and the provider agree the scope first, the apps, APIs, cloud, and user roles, and the fee is locked in before anyone starts. It is a builder quoting a defined job instead of charging by the hour. You get budget certainty, a vendor paid for the result rather than the clock, and a single clean figure that finance and an auditor can both read. The one trade-off is discipline up front: if you add systems mid-engagement, that is a change order, priced and agreed like the original scope. For a test you can describe, this is almost always the model to pick.
The Model Matters More Than the Number
The billing choice matters because the figure on the quote is not the whole story. The model you choose also decides three things that shape what you end up paying:
- Whether the final bill is predictable, or something you only learn once the work is finished.
- Whether the vendor is paid to work efficiently, or to run up more hours.
- Whether you can end up paying for testing you never use.
The Three Models Side by Side
The table below rates the three models on the things that decide your cost and your experience, not just the figure on the quote.
| Fixed-price | Hourly | Credit-based | |
| How you pay | One agreed fee for a set scope | By the hour, as work is done | A prepaid bucket of credits spent over a year |
| Budget predictability | Full, known before you start | Low, known only at the end | Partial, the spend is capped but each credit’s value is fuzzy |
| Vendor’s incentive | Find and fix efficiently | Bill more hours | Sell a bigger bucket |
| Flexibility | Low once the scope is set | High for unknown scope | High across many test types |
| Waste risk | Low | Overruns, with no ceiling | Unused credits expire |
| Easy to compare quotes | Yes, a single clear number | Hard, the final total is unknown | Hard, credits are not standard between vendors |
| Best for | A defined test or a compliance deadline | Open-ended, unscoped research | Large enterprises testing constantly |
How to Choose Your Model
One question settles it for most buyers: can you describe what you want tested? If you can name the apps, APIs, and cloud accounts in scope, you can get a fixed price for them, and you should. A clear scope plus a fixed fee gives you a predictable number, a vendor whose pay does not grow the longer they take, and a clean report an auditor or customer can trust. For most companies, a defined test or a looming SOC 2, ISO 27001, or PCI deadline, that is the whole decision.
The other two models earn their place only in specific cases.
Choose hourly when the scope genuinely cannot be pinned down, such as an open-ended research project or a first look at an unfamiliar system. If you go this route, protect yourself: agree a cap or a not-to-exceed figure up front, so the meter has a limit even when the work does not.
Choose credit-based when you are a large organization running many different tests all year and you are confident you will spend what you buy. The model only pays off if the credits get used. If they tend to sit idle until they expire, a few fixed-price tests will cost less and deliver more.
What Actually Drives the Price
The model decides how you pay. Scope decides how much. Whichever model you land on, the same handful of factors move the final number, and knowing them helps you read a quote and spot where one vendor looks cheaper only because it is doing less.
- Scope. The biggest lever by far: how many web apps, APIs, and cloud accounts are in the test, and how big the network is. More surface to cover means more time, and more cost.
- Depth and user roles. A quick look at the login page costs less than testing everything behind it. Most of the serious risk lives in authenticated areas, the parts you reach after logging in, so testing several user roles properly adds to the price and to the value.
- Retesting and fix support. Some quotes end when the report lands. Others include help fixing the findings and a retest to confirm each one held. The second kind looks pricier up front and usually costs less once you count the work you would otherwise repeat.
- The report. An audit-ready report mapped to your compliance framework takes more effort than a raw tool export, and it is the thing an auditor or customer will accept.
What You Get With CYBRI
CYBRI runs on transparent, fixed pricing, for a simple reason: it keeps your budget predictable and pays the testers for what they find, not for how long they take. There is no hourly meter, and no credits to decode. Every engagement includes:
- One fixed price, whether you test once or all year. CYBRI prices from a clear menu, so you set the scope and goals and know the cost before you buy. A single test is one fixed fee; for ongoing needs, an annual plan fixes the price across a defined set of tests, each one a whole test with its own report, alongside a continuous subscription for always-on coverage. It is the same price list a credit model wraps up and keeps vague, just left out in the open.
- Senior, OSCP-certified testers (OSCP is a hands-on offensive-security certification), two to three per project, working manual-first.
- Reports for two audiences, a plain-language summary for leadership and auditors, plus a technical section for the team doing the fixes, mapped to SOC 2, ISO 27001, PCI DSS, or HIPAA.
- Remediation support and retesting for about three months after the report, so findings get fixed and confirmed, not just listed.
- One live dashboard, Blue Box, keeping findings, retests, and progress in one place you can check any time.
To turn a defined scope into a fixed quote, tell CYBRI what you need.
Frequently Asked Questions
Is PTaaS cheaper than a traditional penetration test?
Not automatically. For the same scope, a PTaaS test and a traditional one-off test cost about the same. PTaaS tends to work out cheaper over time, because retests and tracking are built into the service instead of being re-scoped and re-quoted each round. What moves the price is the scope and the pricing model, not the PTaaS label itself.
Why do penetration test quotes vary so much between providers?
Mostly because they are not quoting the same thing. Quotes differ on how much is in scope, how deep the testing goes, how senior the testers are, and whether fixing support, retesting, and an audit-ready report are included. The pricing model adds more variation on top. Compare quotes on what each one covers, not on the figure at the bottom.
Can I start with one test and add more later?
Yes. Most buyers start with a single fixed-price test on a defined scope, then move to a set of prepaid tests or a continuous plan once they know how often they need to test. Starting small is the normal path, not a limitation.
Get One Clear Number
Whichever model fits your situation, you should know the full cost up front. If you can describe what needs testing, CYBRI will scope it and send back a single fixed quote, with no meter running and no credits to track. Book a scoping call to get your number.