The pentest report came back with two high-severity findings, and engineering closed both tickets within a month. Then the auditor asks how anyone knows the fixes work, and the only thing on file is a ticket marked done. Remediation testing fills that gap. This guide covers what a retest proves, how it differs from remediation support, who needs one, and what happens to findings that can’t be fixed in time.
Quick Answers
What is remediation testing?
After your team fixes a finding from a penetration test (an authorized, simulated attack on your systems), the testers run the same attack again to confirm it no longer works. Each result then goes into an updated report. Most people call this a retest.
Who needs it?
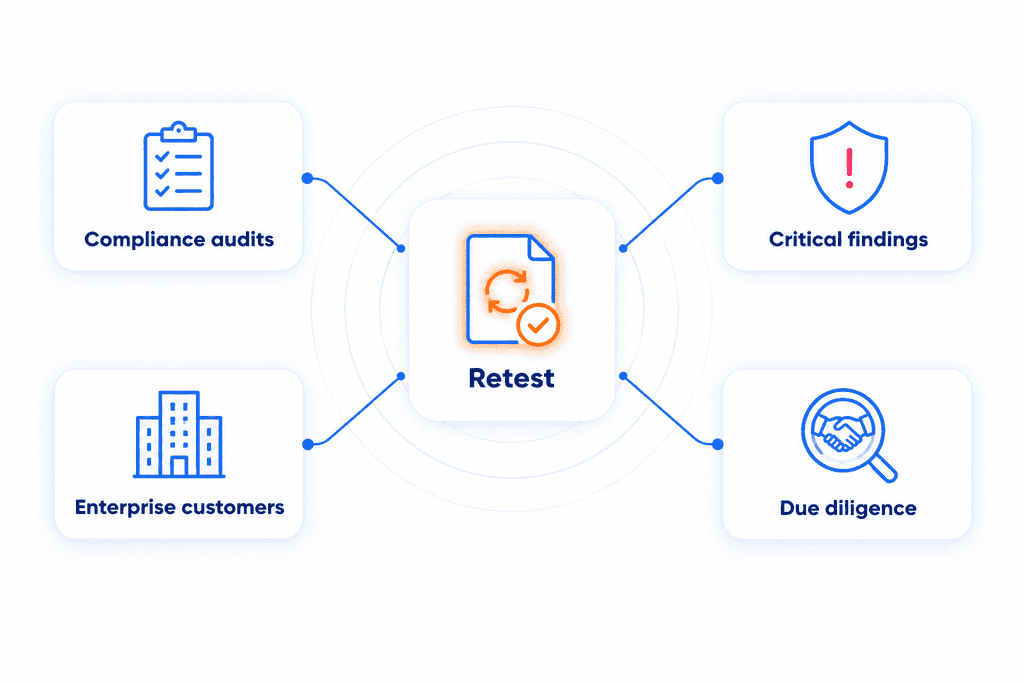
Any company whose pentest report will land in front of an auditor, an enterprise customer, or an insurer. The same goes for any report with critical or high findings, because those fixes carry the most risk and are the likeliest to close one hole while leaving the same flaw open somewhere nearby.
Is a retest included in a pentest?
That depends on the provider. Some sell it as a separate service with its own fee, and others build it into the engagement. CYBRI includes remediation support and a retest inside a 90-day window in every quote, and the updated report goes into the audit file as evidence that the findings were fixed.
What a Retest Proves
A ticket marked done is a developer’s claim, not proof. The proof is a tester running the original attack again and watching it fail.
Fixes tend to cover the exact spot the report pointed at. Say a customer could open someone else’s invoice by changing a number in the URL, a classic IDOR flaw. The developer locks down that page, but the download button runs through different code and hands the PDF to anyone. A retest tries those neighboring paths, and it catches fixes that broke something else along the way.
Remediation Support and Remediation Testing
Both happen in the months after the report. Remediation support is help during the fix: testers explain findings, walk engineers through how the attack worked, and review a proposed fix before it ships. Remediation testing starts once the fix is live: a tester repeats the attack, and the updated report either marks the finding resolved or sends it back.
Good support means fewer failed retests. Many providers include one retest and leave support out, so engineers get a PDF and nobody to call. Check the quote for both.
Who Needs Remediation Testing
If anyone outside the company will read the report, plan for a retest.
- Compliance audits. PCI DSS, the standard for companies that handle card payments, requires it outright: Requirement 11.4.4 says findings get fixed and testing is repeated to verify. SOC 2 and ISO 27001 don’t name a retest, though auditors ask for proof that findings were addressed, usually a retest report or a documented risk acceptance.
- Enterprise customers. Security reviews ask for the latest report, and open criticals stall them. An updated report showing them resolved ends the questions.
- Critical or high findings, especially access-control flaws, which are the fixes most likely to be partial.
- Due diligence and insurance renewals, where buyers and insurers ask whether known issues were closed.
When Fixes Take Longer, and When Risk Gets Accepted
Some fixes need a database migration or an update from a vendor, and those take time. Most teams set deadlines by severity: days for critical, months for low.
Other findings stay open on purpose, like a low-impact issue on an internal admin page or a flaw in a feature being retired next quarter. Risk acceptance (a recorded decision to keep a known issue open) is a normal outcome when it has an owner, a reason, a review date, and sign-off from someone with authority. Auditors accept a documented exception far more readily than an open finding with no record.
The retest confirms everything that was fixed, and the updated report lists the rest as accepted or in progress.
Remediation Testing With CYBRI
If your report is headed to an auditor or a customer’s security team, the retest matters as much as the test itself. CYBRI builds remediation testing into every quote, so no second invoice shows up when the fixes are ready. The fix window runs 90 days, long enough for a migration or a vendor update, and the testers stay reachable the whole time.
Every engagement includes:
- Senior, OSCP-certified testers working manual-first
- Gray box testing by default, with a login for every user role in scope
- Same-day alerts for critical findings, ahead of the full report
- A report for two audiences: a plain-language summary for leadership and auditors, plus technical findings scored on CVSS 4.0 (the standard severity scale) with fix steps for each
- Findings mapped to your framework, including SOC 2, ISO 27001, HIPAA, and PCI DSS
- Remediation support through the fix window, with testers answering questions and reviewing fixes before they ship
- An updated report showing each finding as resolved, accepted, or open, ready for the audit file as compliance evidence
- Blue Box tracking of findings and retests for clients on ongoing programs
Contact CYBRI to scope a test with remediation testing built in.
Frequently Asked Questions
Is remediation testing included in a CYBRI pentest?
Yes. Remediation support and a retest inside the 90-day window are part of the quote.
Does a passed retest mean the app is secure?
It means the findings from the original report are closed. New features, and anything the first test missed, need the next full test.
What if a fix isn’t ready before the window closes?
Tell the testers early. Extended retest windows are available as an add-on, and a finding that has to wait can be documented as an accepted risk with an owner and a review date, then shown as open in the updated report.
Get the Fixes Verified Before the Auditor Asks
Your last pentest report, or a rough list of what’s in scope, is enough for the first call. The call works out what needs testing and how to time it so the retested report is ready before your audit or customer review. Book a scoping call with CYBRI.