The GDPR never uses the words “penetration test” in its security article. What Article 32 does require is a process for regularly testing whether your security measures work, and the accountability principle requires you to be able to show it. A penetration test is the most direct way to do both: testers attack the systems that hold personal data, and the report records what they could reach. This guide covers what the regulation says, what a GDPR-focused test should cover, how personal data is handled during the test, and what the report needs to contain. It is practical guidance, not legal advice, so confirm how it applies to you with your privacy counsel or data protection officer.
Quick Answers
Does GDPR require penetration testing?
Not by name. Article 32(1)(d) requires “a process for regularly testing, assessing and evaluating the effectiveness of technical and organisational measures”. The regulation leaves the method to you, and a penetration test is a widely used way to meet it.
How often should you test?
The GDPR sets no frequency. Testing should follow your risk: how much personal data you hold, how sensitive it is, and how often your systems change. Once a year and after major changes is common practice, not a legal minimum.
Does the test have to be done by an outside firm?
No. The regulation doesn’t say who must do the testing. An independent tester is easier to defend to a customer or regulator, because the people who built a system rarely find their own mistakes.
What the GDPR Says About Security Testing
These are the provisions a penetration test connects to. The wording in quotes is from the regulation.
| Provision | What it says | What it means for testing |
| Article 32(1) | Controllers and processors must implement measures “to ensure a level of security appropriate to the risk” | Security is judged against your risk, not a fixed checklist |
| Article 32(1)(d) | “a process for regularly testing, assessing and evaluating the effectiveness” of those measures | You need a repeatable testing process and a record of it |
| Article 5(2) | The controller must “be able to demonstrate compliance” | A dated report with findings and retests is that evidence |
| Article 25 | Data protection by design and by default | A test shows whether the designed controls hold up in practice |
| Article 28 | The contract with a processor must require it to take “all measures required pursuant to Article 32” and to support audits | Customers can ask a SaaS vendor for proof of testing |
| Article 35 | A data protection impact assessment must list “safeguards, security measures” for high-risk processing | Test results give the assessment real evidence |
| Article 33 | A breach must be reported “not later than 72 hours after having become aware of it”, where feasible | Finding the flaw first is cheaper than reporting the breach |
Two points are often misstated. First, an infringement of Article 32 falls in the lower fine tier of Article 83: up to €10 million or 2% of worldwide annual turnover, whichever is higher. The higher tier, up to €20 million or 4%, covers the basic principles in Article 5, which include the security principle, so a serious security failure can be pursued under either.
Second, regulators confirm that the method is yours to choose. The UK Information Commissioner’s Office says testing can be done “through a number of techniques, such as vulnerability scanning and penetration testing”, and that the law “does not specify the type of testing, nor how regularly you should undertake it”. It adds that whatever testing you do, “you should document the results”. That guidance covers the UK GDPR, which keeps the same wording for the testing requirement in Article 32(1)(d), and was under review at the time of writing.
What a GDPR Penetration Test Should Cover
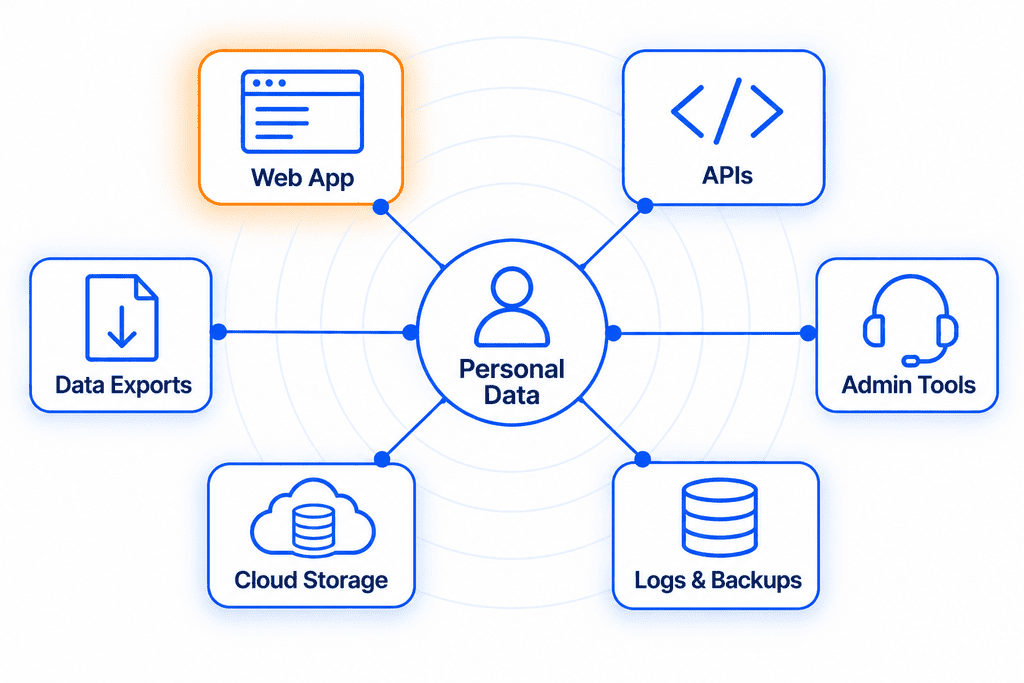
Scope a GDPR test from the data, not from the server list. Start with your record of processing activities (Article 30), find every system that stores or moves personal data, and test those.
| Where personal data lives | What testers check |
| Web application | Whether one user or customer can read another’s records, and whether a low-privilege role can reach data reserved for admins |
| APIs | Endpoints that return more personal data than the screen shows, and record IDs that can be changed to pull someone else’s data |
| Data export and deletion features | Whether the tools built for access and erasure requests can be used to export or delete another person’s data |
| Admin and support tools | How much customer data staff accounts can reach, and whether that access is logged |
| Cloud storage and databases | Public buckets, exposed backups, and databases reachable from the internet |
| Login and sessions | Password reset flows, session handling, and missing multi-factor authentication on accounts that hold personal data |
| Logs and backups | Personal data copied into places with weaker protection than the main database |
| Third-party integrations | How your product is configured and connected to subprocessors. The vendor’s own systems stay out unless it gives permission |
Give testers a login for each user role. The flaws that matter most under the GDPR, one person reaching another person’s data, sit behind the login, which is why gray box testing is the usual choice.
Handling Personal Data During the Test
A penetration test can itself touch personal data, so plan for that before it starts:
- Use a test environment with synthetic data where you can. It has to mirror production closely: same access model, same configuration.
- Put a contract in place if testers will see real personal data. A tester who can access live records on your behalf may be acting as your processor, and if so Article 28 calls for a data processing agreement. Confirm this with your counsel before testing starts.
- Prove access, don’t collect data. Good practice is to show that a record could be reached, with one redacted example, and stop there.
- Keep personal data out of the report. Screenshots and evidence should be masked.
- Agree what happens to evidence afterward. Set a retention period and confirm deletion.
How a GDPR Penetration Test Runs
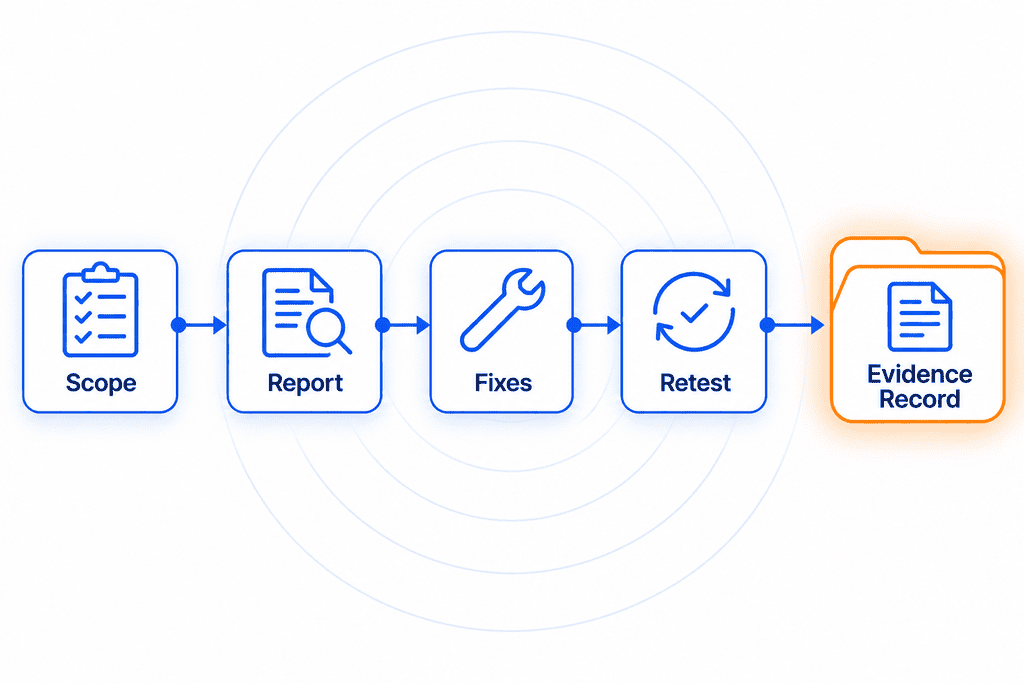
- Scoping and data mapping. Agree which systems, data types, and user roles are in scope, and which subprocessors sit around them.
- Preparation. Share architecture notes and API documentation, set up test accounts for each role, and sign the rules of engagement.
- Testing. Senior testers work manually across the agreed apps, APIs, cloud, and network, following recognized methods such as the OWASP testing guides and NIST guidance. Automated scans support the work but don’t replace it.
- Same-day alerts. Anything that exposes personal data and can be exploited is flagged at once, ahead of the report.
- Reporting. Findings are written up with the data affected and the fix, then walked through on a call.
- Remediation and retesting. Your team fixes, the testers re-run the attacks, and the report is updated with each finding’s final status.
What the Report Should Contain
A GDPR-ready report answers the questions a customer, auditor, or regulator will ask:
- A plain-language summary of what was tested, when, and the overall result
- Scope, methodology, and anything excluded
- Each finding with its severity, the proof, and a fix
- The personal data each finding exposes, and roughly how many people it affects
- The GDPR provision each finding relates to
- Retest results showing which findings are closed
Here is how a single finding should read:
| Field | Example |
| Finding | Customer invoices can be read across accounts |
| Severity | High |
| What was proven | A standard user changed the invoice number in a request and received another customer’s invoice |
| Personal data exposed | Names, billing addresses, and email addresses for every customer with an invoice |
| GDPR relevance | Article 32(1)(b), confidentiality of processing. Exploited by a real attacker, this would be a personal data breach to assess under Article 33 |
| Fix | Check on the server that the invoice belongs to the requesting account |
| Retest | Fixed, verified 14 days after the report |
Keep the report with the scope document, the remediation tickets, and the retest result. Together they form the record Article 5(2) expects you to be able to produce. CYBRI’s guide to what a penetration testing report includes goes through each section, and the remediation testing guide explains the retest.
When to Test
There is no legal schedule, so tie testing to change and risk:
- At least once a year for systems holding personal data, as common practice
- After major changes, such as a new feature, a cloud migration, or a new subprocessor
- When a new data flow or a more sensitive data type is added
- Before a launch in the EU or UK, or ahead of a customer’s vendor review
- When a data protection impact assessment or an incident points to higher risk
What a Penetration Test Doesn’t Cover
A penetration test is evidence for the security parts of the GDPR, not for the whole regulation. It says nothing about your lawful basis for processing, retention periods, or how you answer access requests. It is also a point-in-time check, so it works best alongside vulnerability scanning, secure development practices, patching, and monitoring between tests.
GDPR Penetration Testing With CYBRI
CYBRI runs manual-first testing with senior, US-based, OSCP-certified testers, starting from a login for each user role. Scope is built around where your personal data lives, across web apps, APIs, cloud, and network. Critical findings are flagged the same day.
Reports pair a plain-language summary with technical findings and fix steps, and map findings to GDPR alongside SOC 2, ISO 27001, PCI DSS, and HIPAA, so one test can serve more than one audit. Remediation support and a retest inside a 90-day window are part of the quote, which gives you the dated record of fixes that accountability calls for. See CYBRI’s GDPR penetration testing services, or contact CYBRI to scope a test.
Frequently Asked Questions
Is a vulnerability scan enough for GDPR?
The regulation doesn’t rule it out, and a scan is a valid part of a testing process. On its own it only finds known weaknesses. It can’t show whether one customer can read another’s data, which is the kind of flaw that leads to a reportable breach.
Can our internal team do the testing?
Yes, the GDPR doesn’t forbid it. Internal testing is useful between external tests. For customers and regulators, an independent report carries more weight than a team checking its own work.
Does the UK GDPR differ?
Not on this point. The UK GDPR keeps the same testing requirement in Article 32(1)(d), and the ICO’s guidance names vulnerability scanning and penetration testing as ways to test security measures without requiring either.
If a test finds exposed personal data, is that a breach we have to report?
An authorized tester proving that data could be reached is generally treated as a finding, not automatically a breach. If the test turns up signs that someone else already got in, the 72-hour clock in Article 33 starts when you become aware. Involve your data protection officer or counsel as soon as that question comes up.
Do we have to fix everything the test finds?
The GDPR doesn’t list which findings to fix or by when. It expects security appropriate to the risk, so leaving a known, serious flaw open is hard to defend. Fix critical and high findings first, record the decision on the rest, and keep the retest result.
Get a Quote for a GDPR-Focused Test
A list of the systems that hold personal data, your user roles, and the customer or audit behind the test is enough to start. CYBRI turns that into a written scope and a fixed-price quote. Book a scoping call with CYBRI.