
Penetration Testing Company - CYBRI

Manual-first penetration testing for Applications, APIs, Cloud, and Networks

Find & Fix Security Vulnerabilities with Manual-First Expert Testing

OSCP-Certified Experts | Remediation Testing & Support | Compliance-Ready Reports.

9 Years Dedicated To Penetration Testing

Since 2017, CYBRI has focused exclusively on penetration testing and vulnerability scanning, helping businesses from startups to multinational enterprises identify and eliminate security vulnerabilities. Our Certified Experts structure every engagement around OWASP and NIST, covering web and mobile apps, cloud, APIs, and networks. All findings are classified against CWE and cite relevant CVEs where known vulnerabilities apply, and all results map to compliance and audit requirements including SOC 2, ISO 27001, GDPR, HIPAA, and PCI DSS.

mypostcard_testimonial_logo_tn_color
ICAHN ENTERPRISES L.P.
tristar-logo
HealthCare.com
cylera-ps-1
cherre-logo-ps
Penetration Testing

Our Penetration Testing Services

icon

Identify application logic weaknesses and OWASP Top 10 vulnerabilities, tested from a login for each user role.

icon

Test iOS and Android apps, their on-device data storage, and the APIs behind them against the OWASP Mobile Top 10.

icon

Discover security gaps that may exist over the LAN and outside your company network.

icon

Pen test your API to prevent bad actors from using this as an attack vector against your company.

icon

AI agents can interact with applications, APIs, databases, files, and external tools, creating additional attack paths beyond the underlying model

icon

Decrease threats to your web applications and cloud environment hosted on AWS, Azure, and Google Cloud Platform.
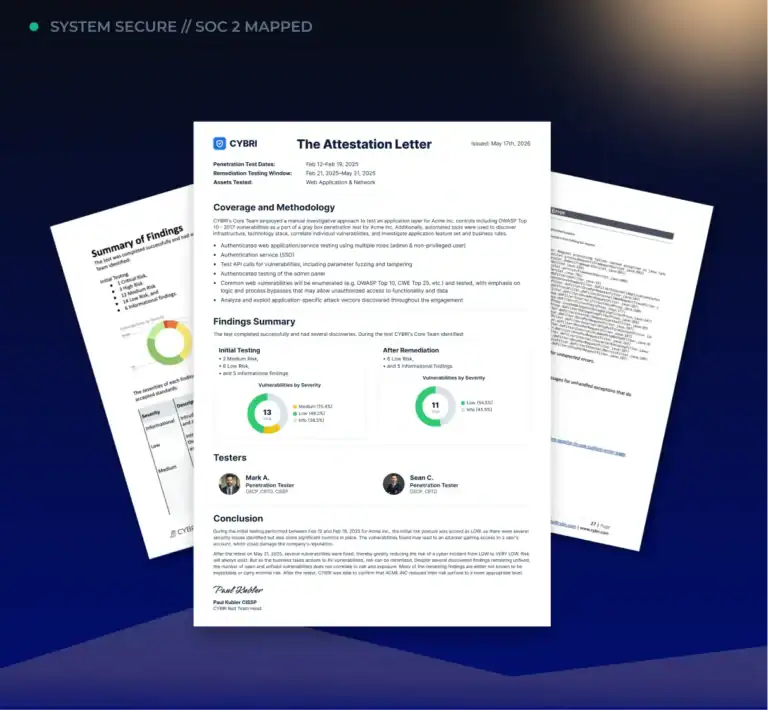
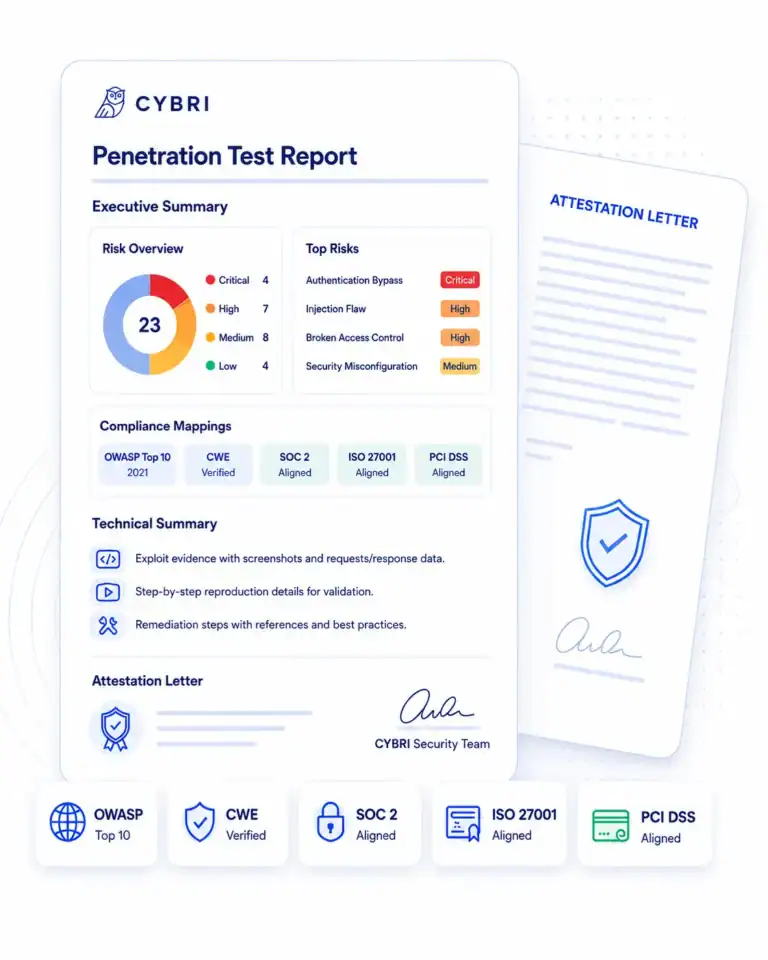
Reporting & Attestation

We specialize in supporting SOC 2, ISO 27001, HIPAA, PCI DSS, GDPR, NYDFS, and other compliance requirements through comprehensive security testing and reporting.

Compliance Testing

We specialize in supporting SOC 2, ISO 27001, HIPAA, PCI DSS, GDPR, NYDFS, and other compliance requirements through comprehensive security testing and reporting.

SOC 2

Confirm that your controls work against the Trust Services Criteria, provide an audit-ready report and letter of attestation.

Test every system that stores or moves patient data, with findings mapped to the HIPAA Security Rule and HITRUST.

Show that your Annex A controls hold up under real attacks, with evidence ready for certification and surveillance audits.

Meet PCI DSS Requirement 11.4 with internal, external, and segmentation testing of your cardholder data environment.

Test the systems that hold personal data, with findings mapped to Article 32 and written for your DPO.

Test the systems that hold client and financial data, with reports that support SEC and FINRA cybersecurity reviews.

Our methodologies

Our certified experts deliver manual penetration testing aligned with OWASP across API, Web, Mobile, Cloud, and AI. CWE and CVE findings are delivered via our PTaaS platform, and we also offer continuous coverage through our proprietary technology.

icon

Our certified testers work hands-on to work through your application, and to chain logic errors and access issues the same way that a hacker would with findings delivered via BlueBox.

SOC 2
icon

We test for the most critical vulnerability and security risks according to the modern frameworks like OWASP for API, Web, Mobile, Cloud, AI with findings reported as CWE and CVE
HIPAA
logo-svss
logo-cwe
logo-owasp

How CYBRI Delivers Your Testing

icon

One-off, point in time testing Retesting support Remediation support throughout the engagemen

icon

Designed for companies requiring multiple manual tests throughout the year Delivered via a centralized tracking, messaging, and reporting platform

icon

Designed for teams with more aggressive release cycles Continuous engagements using proprietary technology (WraithScan)

METHODOLOGY

How CYBRI Penetration Testing Works

Discovery

CYBRI penetration tests are run by senior, OSCP-certified testers who work manual-first. You pay a fixed price per test and can test as often as your releases need.

We will collect the needed information from you and your team to make sure that the right assets are being tested and the right team is assigned.
RED TEAM IN ACTION
CYBRI penetration tests are run by senior, OSCP-certified testers who work manual-first. You pay a fixed price per test and can test as often as your releases need.
CYBRI Red Team members will start testing your infrastructure and will ensure coverage of the OWASP Top 10 vulnerabilities. They will use their own techniques to ensure the highest levels and standards of testing.
Reporting
CYBRI penetration tests are run by senior, OSCP-certified testers who work manual-first. You pay a fixed price per test and can test as often as your releases need.
After each finding is verified by our Red Team members, they get submitted into your dashboard and report. Upon completion of each test, you will have a clear report that can be shared with executive and technical members as well as your clients.
Collaboration
CYBRI penetration tests are run by senior, OSCP-certified testers who work manual-first. You pay a fixed price per test and can test as often as your releases need.
Communicate with CYBRI Red Team members about your vulnerabilities and assign them to your team members for remediation. Our platform has a clear collaboration functionality to help your team with remediation of the findings.
Retest
CYBRI penetration tests are run by senior, OSCP-certified testers who work manual-first. You pay a fixed price per test and can test as often as your releases need.
Once your team has fixed the findings, our testers re-run the original attacks to confirm each fix holds. Remediation support and a retest inside a 90-day window are part of the quote, and you get an updated report showing the final status of every finding.
REPEAT
CYBRI penetration tests are run by senior, OSCP-certified testers who work manual-first. You pay a fixed price per test and can test as often as your releases need.
Improve your risk posture and reduce your organization’s liability. Assess your security on a yearly basis, or test continuously as your product changes, with the same senior CYBRI team that knows your environment.
01 Discovery
Discovery
CYBRI penetration tests are run by senior, OSCP-certified testers who work manual-first. You pay a fixed price per test and can test as often as your releases need.
We will collect the needed information from you and your team to make sure that the right assets are being tested and the right team is assigned.
RED TEAM IN ACTION
CYBRI penetration tests are run by senior, OSCP-certified testers who work manual-first. You pay a fixed price per test and can test as often as your releases need.
CYBRI Red Team members will start testing your infrastructure and will ensure coverage of the OWASP Top 10 vulnerabilities. They will use their own techniques to ensure the highest levels and standards of testing.
Reporting
CYBRI penetration tests are run by senior, OSCP-certified testers who work manual-first. You pay a fixed price per test and can test as often as your releases need.
After each finding is verified by our Red Team members, they get submitted into your dashboard and report. Upon completion of each test, you will have a clear report that can be shared with executive and technical members as well as your clients.
Collaboration
CYBRI penetration tests are run by senior, OSCP-certified testers who work manual-first. You pay a fixed price per test and can test as often as your releases need.
Communicate with CYBRI Red Team members about your vulnerabilities and assign them to your team members for remediation. Our platform has a clear collaboration functionality to help your team with remediation of the findings.
Retest
CYBRI penetration tests are run by senior, OSCP-certified testers who work manual-first. You pay a fixed price per test and can test as often as your releases need.
Once your team has fixed the findings, our testers re-run the original attacks to confirm each fix holds. Remediation support and a retest inside a 90-day window are part of the quote, and you get an updated report showing the final status of every finding.
REPEAT
CYBRI penetration tests are run by senior, OSCP-certified testers who work manual-first. You pay a fixed price per test and can test as often as your releases need.
Improve your risk posture and reduce your organization’s liability. Assess your security on a yearly basis, or test continuously as your product changes, with the same senior CYBRI team that knows your environment.

Client Testimonials

What Our Customers Have to Say

Insights & Resources

9 Years Dedicated To Penetration Testing

Since 2017, CYBRI has been dedicated to penetration testing, helping businesses of all sizes, from startups to multinational enterprises, identify and eliminate security vulnerabilities. Our sole focus is pentesting and vulnerability scanning, ensuring deep expertise and rigorous assessments without distractions.
Michael B.
Michael B.Managing Partner, Barasch & McGarry
I am an attorney who represents thousands of people in the 9/11 community. CYBRI helped my company resolve several cybersecurity issues. I definitely recommend working with CYBRI.
Tim O.
Tim O.CEO at Cylera
I’m using CYBRI and have been very impressed with the experience and quality of the experts and CYBRI’s customer service. It has been a super seamless process that I’m happy and pleased with – I recommend CYBRI to all businesses.
Sergio V.
Sergio V.CTO at HealthCare.com
I hired CYBRI to help my company with various cybersecurity services, specifically HIPAA and CCPA. I have been satisfied with the quality of work performed by the cybersecurity expert. The customer service is excellent. I would recommend CYBRI for all of your cybersecurity needs.
L.D. Salmanson
L.D. SalmansonCEO at Cherre.com
We worked with CYBRI on assessing vulnerabilities and understanding the risks of our client-facing web assets. We are satisfied with the results and the professionalism of the Red Team members. Highly recommend CYBRI to all businesses.
Marco Huslmann
Marco HuslmannCTO MyPostcard
CYBRI is a great solution that helps streamline the penetration testing process. I strongly recommend them and will work with them again.
Alex Rothberg
Alex RothbergCTO IntusCare
I highly recommend CBYRI to businesses that need penetration testing to ensure their business infrastructure is secure.
John Tambuting
John TambutingCTO Pangea.app
I am confident CYBRI is the right penetration testing choice if you are looking to build a secure business environment.

Discuss Your Project


    Frequently asked questions

    Typically, an engagement lasts between 1.5 to 3 weeks. For larger scope engagements, pentests can last longer.

    Most penetration tests cost between $5,000 and $50,000 or more. For a full breakdown, you can read our comprehensive guide.

    We run manual-first testing aligned with OWASP and NIST, classifying findings against CWE and citing relevant CVEs where they apply.

    Yes, we provide an attestation letter summarizing the scope and results that you can share with customers and auditors.

    Yes, we test AI and LLM features for risks like prompt injection and data leakage, along with other issues specific to how these systems behave.

    Remediation retesting is included for engagements above 6,000 USD, confirming your fixes.

    Yes, we can share a sample report so you can see exactly how we document and prioritize findings. In addition, you’ll see a detailed explanation of our process, methodology, tools we use, as well as delivery models. We believe in full transparency.

    Yes, every finding maps to the compliance frameworks you need, including SOC 2, ISO 27001, HIPAA, GDPR and others.

    Yes, every tester on your engagement holds advanced offensive-security certifications such as OSCP, OSWE, GIAC, or CISSP.

    Looking for your next penetration testing quote?

    Get a proposal from a team specializing in manual-first penetration testing for web applications, APIs, cloud, and network environments.