
Manual-first penetration testing for Applications, APIs, Cloud, and Networks
Find & Fix Security Vulnerabilities with Manual-First Expert Testing
9 Years Dedicated To Penetration Testing
Since 2017, CYBRI has focused exclusively on penetration testing and vulnerability scanning, helping businesses from startups to multinational enterprises identify and eliminate security vulnerabilities. Our Certified Experts structure every engagement around OWASP and NIST, covering web and mobile apps, cloud, APIs, and networks. All findings are classified against CWE and cite relevant CVEs where known vulnerabilities apply, and all results map to compliance and audit requirements including SOC 2, ISO 27001, GDPR, HIPAA, and PCI DSS.
Our Penetration Testing Services


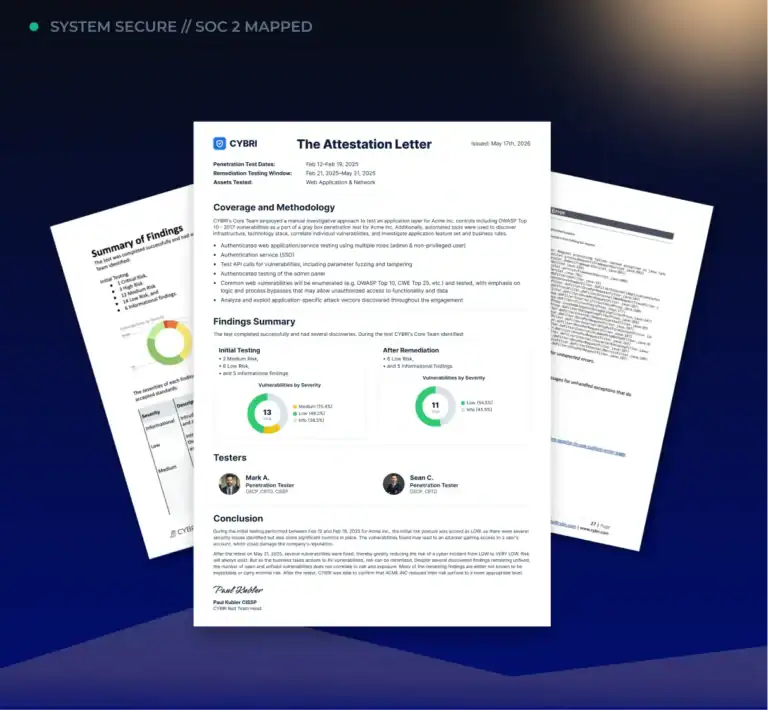
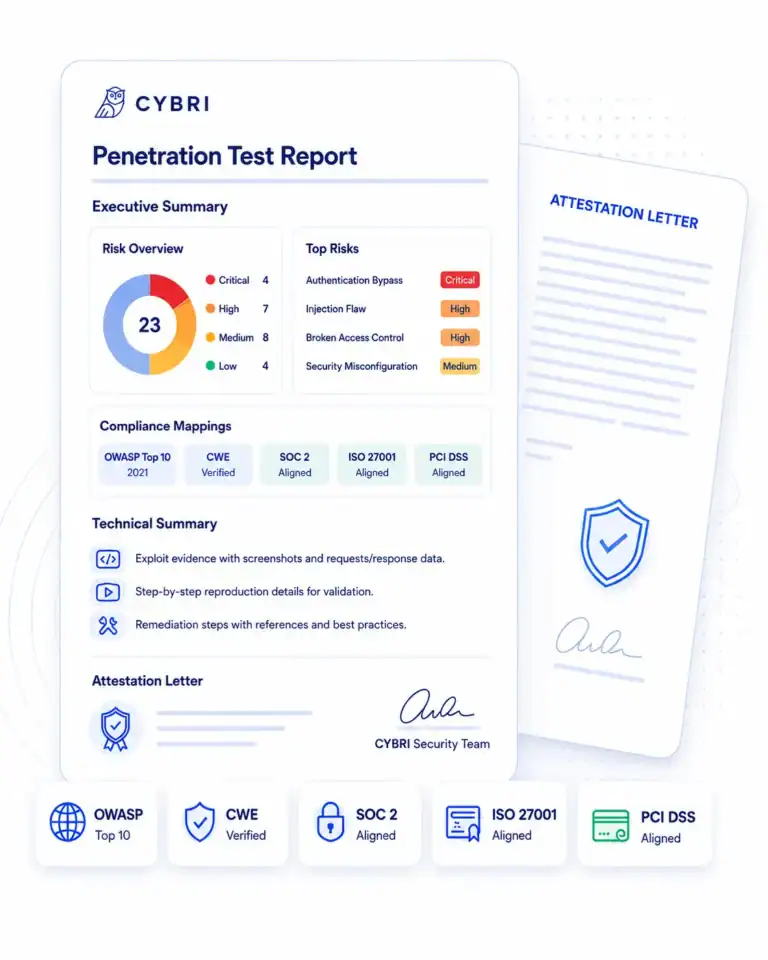
Reporting & Attestation
We specialize in supporting SOC 2, ISO 27001, HIPAA, PCI DSS, GDPR, NYDFS, and other compliance requirements through comprehensive security testing and reporting.
- Executive summary report with detailed risk and severity profile with required compliance mappings
- Technical summary report with detailed evidence of each exploit that our team discovered during the engagement with remediation steps required to replicate and resolve vulnerabilities
- Attestation letter that can be shared with auditors, clients and also proves your enhanced security to your customers.
Compliance Testing
We specialize in supporting SOC 2, ISO 27001, HIPAA, PCI DSS, GDPR, NYDFS, and other compliance requirements through comprehensive security testing and reporting.
SOC 2
Confirm that your controls work against the Trust Services Criteria, provide an audit-ready report and letter of attestation.
HIPAA
Test every system that stores or moves patient data, with findings mapped to the HIPAA Security Rule and HITRUST.
ISO 27001
Show that your Annex A controls hold up under real attacks, with evidence ready for certification and surveillance audits.
PCI DSS
Meet PCI DSS Requirement 11.4 with internal, external, and segmentation testing of your cardholder data environment.
GDPR
Test the systems that hold personal data, with findings mapped to Article 32 and written for your DPO.
SEC & FINRA
Test the systems that hold client and financial data, with reports that support SEC and FINRA cybersecurity reviews.
Our methodologies
Our certified experts deliver manual penetration testing aligned with OWASP across API, Web, Mobile, Cloud, and AI. CWE and CVE findings are delivered via our PTaaS platform, and we also offer continuous coverage through our proprietary technology.
How CYBRI Delivers Your Testing
How CYBRI Penetration Testing Works
CYBRI penetration tests are run by senior, OSCP-certified testers who work manual-first. You pay a fixed price per test and can test as often as your releases need.
01 Discovery
02 Red Team in Action
03 Reporting
04 Collaboration
05 Retest
06 Repeat
Client Testimonials
What Our Customers Have to Say
Insights & Resources
9 Years Dedicated To Penetration Testing
Discuss Your Project
Frequently asked questions
Most penetration tests cost between $5,000 and $50,000 or more. For a full breakdown, you can read our comprehensive guide.
We run manual-first testing aligned with OWASP and NIST, classifying findings against CWE and citing relevant CVEs where they apply.
Yes, we provide an attestation letter summarizing the scope and results that you can share with customers and auditors.
Yes, we test AI and LLM features for risks like prompt injection and data leakage, along with other issues specific to how these systems behave.
Remediation retesting is included for engagements above 6,000 USD, confirming your fixes.
Yes, we can share a sample report so you can see exactly how we document and prioritize findings. In addition, you’ll see a detailed explanation of our process, methodology, tools we use, as well as delivery models. We believe in full transparency.
Yes, every finding maps to the compliance frameworks you need, including SOC 2, ISO 27001, HIPAA, GDPR and others.
Yes, every tester on your engagement holds advanced offensive-security certifications such as OSCP, OSWE, GIAC, or CISSP.